The EU AI Act is a comprehensive, risk-based legal framework for how artificial intelligence is developed, supplied and used in the European Union. Enterprises have to identify their AI systems, classify the risks, work out their legal role and follow phased deadlines, because prohibited practices, general-purpose AI, transparency and high-risk systems each play by different rules.
The usual mistake is treating it as a single deadline that's still far off. Misread the timeline and you might leave live obligations untouched while you wait for high-risk rules that have nothing to do with them.
Which organizations fall within the EU AI Act's scope?
Not only European ones. The trigger is placing an AI system on the EU market, or using one in a way that affects people in the EU. Where your headquarters sits doesn't settle it.
Take a US enterprise. It may be covered if it serves European customers, operates in Europe, or deploys an AI system whose outputs affect people located in the EU. AI product companies hit the same question, and so do service providers installing systems in client environments.
So write it down: where each system is offered, where its outputs are used, whose data it processes, and which legal entity is the provider or deployer. Data location still matters, but it isn't the same as legal sovereignty or regulatory scope. We untangle that in data residency versus data sovereignty.
How does the EU AI Act classify AI systems?
By risk, purpose, capabilities and use, and you should classify before anything else, because the category tells you what to prohibit, disclose, document, test or govern. Four buckets matter for enterprise planning.
Prohibited practices come first. Think prohibited forms of social scoring, harmful subliminal manipulation, and certain real-time remote biometric identification by law enforcement in publicly accessible spaces without the required authorization or exception.
General-purpose AI covers foundation models and large language models that can support many downstream applications. Obligations can land on the organizations providing these models, with extra considerations for models presenting systemic risk.
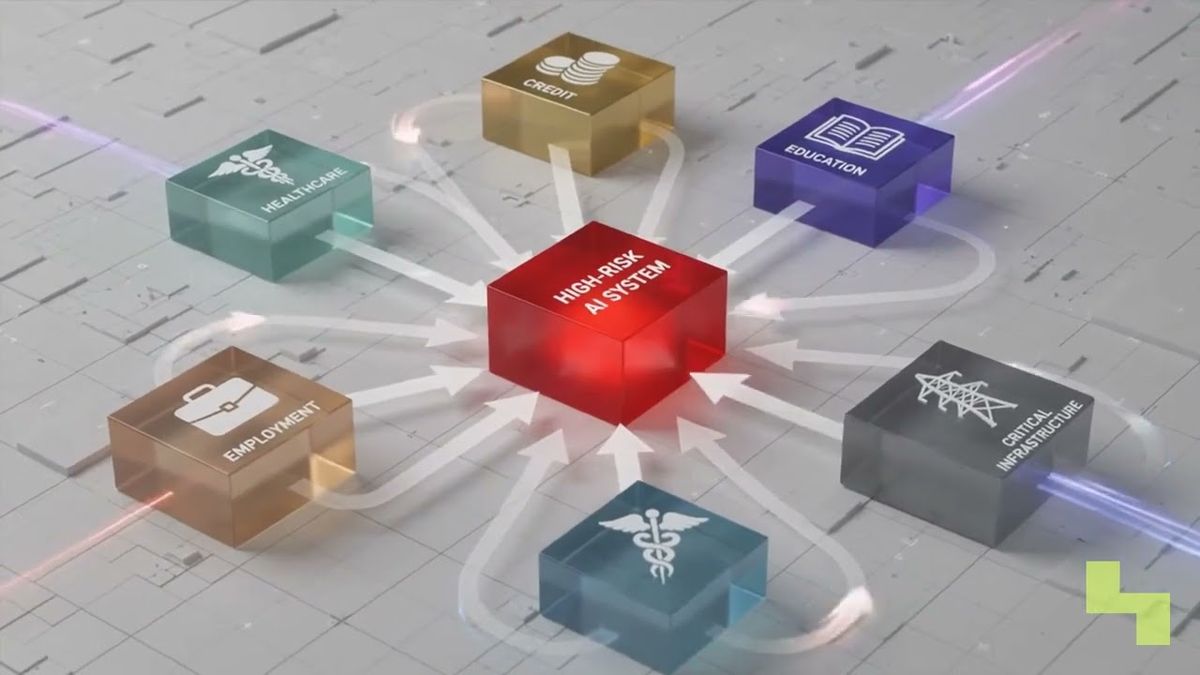
Then there are transparency-regulated systems: users may need to know they're talking to a chatbot, looking at AI-generated content, or subject to emotion detection or recognition technology. Last come high-risk systems, listed in Annex III, which means specified uses in areas such as employment, credit decisions, healthcare diagnostics, education and law enforcement.
Does using a large language model make your application high risk? Not by itself. What counts is the intended purpose, the deployment context, the effect on people and your organization's legal role. Providers, deployers, importers and distributors can carry different responsibilities.
When do EU AI Act requirements become enforceable?
In phases. The EU AI Act entered into force in August 2024 and has been switching on piece by piece since then, so track the timeline requirement by requirement and not as one date.
- February 2025: bans on prohibited AI practices became applicable.
- August 2025: general-purpose AI model obligations became active.
- August 2026: financial penalties became enforceable for general-purpose AI obligations. Chatbot disclosure, emotion detection labeling and AI-generated content marking requirements also became enforceable.
- December 2027: the Annex III high-risk obligations are scheduled to apply, following the Digital Omnibus amendments formally adopted in June 2026.
That last date is for Annex III systems only. The bans, the general-purpose AI obligations and the transparency requirements are already in force and haven't moved.
The trap is reading the Annex III delay as a general pause. Map every system to its own category and deadline instead.

What does high-risk AI compliance require from enterprises?
Documented controls across design, data, testing, human oversight and deployment. The exact duties depend on the system and on your role, but the AI compliance work should begin well before the Annex III deadline.
For high-risk systems, the core requirements include a documented risk management system kept up through the system lifecycle, and technical documentation of the system's design and intended operation. Data governance has to cover training data quality and bias management. You also need human oversight that fits the decisions and risks involved, testing for accuracy, robustness and relevant failure conditions, and registration in the EU AI database before deployment where required.
Under all of it sits an accurate AI inventory. Each record should say who owns the system, its intended purpose, the models and data involved, who it affects, where it's deployed, your legal role, its risk classification, the deadlines that apply and the evidence you hold.
We'd start there. Without the inventory you can't say which obligations apply, never mind prove you understand your exposure. Then feed that evidence into wider AI audit preparation: access records, approvals, test results, model documentation and change history.

How Hyperlake helps
Hyperlake is the AI cloud for your team and your agents, on your cloud. Teams can deploy and govern data, models, applications and tools in infrastructure they or their clients control. Its shared controls can support authenticated access, scoped policies, audit records, lineage, network isolation, observability and repeatable lifecycle operations. Legal classification and compliance decisions stay with the organization. To talk through an AI environment with governance requirements, talk to our team.
Frequently asked questions
Does the EU AI Act apply to a US company with European customers?
It can. The EU AI Act reaches beyond the EU when an AI system is placed on the EU market, or when its use or outputs affect people in the EU. A US company should check its European customers, operations, users, deployment locations and legal role. Don't assume headquarters keeps you outside the regulation.
Is every enterprise chatbot considered a high-risk AI system?
No, most aren't. A chatbot may face transparency requirements without being an Annex III high-risk system, and it comes down to intended purpose and context. A general customer-support chatbot is one thing; a system that screens employment candidates, assesses credit or supports specified healthcare decisions is another.
Does the Annex III delay mean enterprises can pause EU AI Act work?
No. The move to December 2027 covers only the Annex III high-risk obligations. Prohibited-practice bans, general-purpose AI requirements and transparency duties follow earlier deadlines and are already in force. You still need an inventory, classifications, owners, the disclosures that apply and evidence for whatever affects you now.